US Homeland Security Data Breach Exposes 40,000 Workers
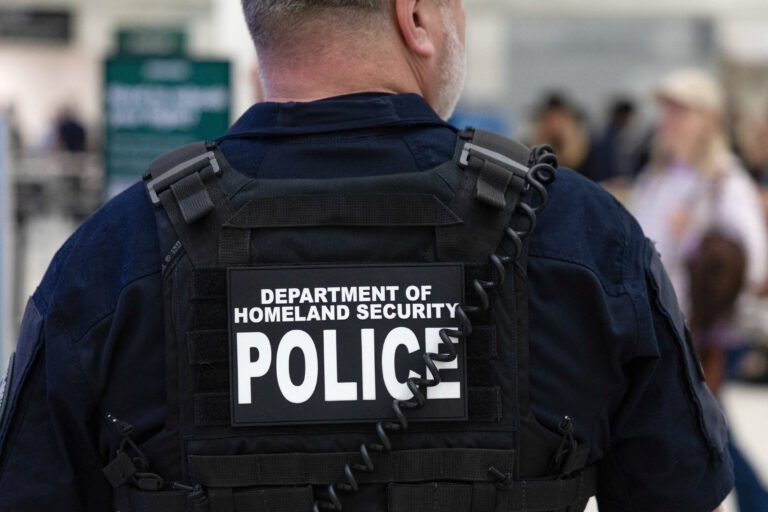
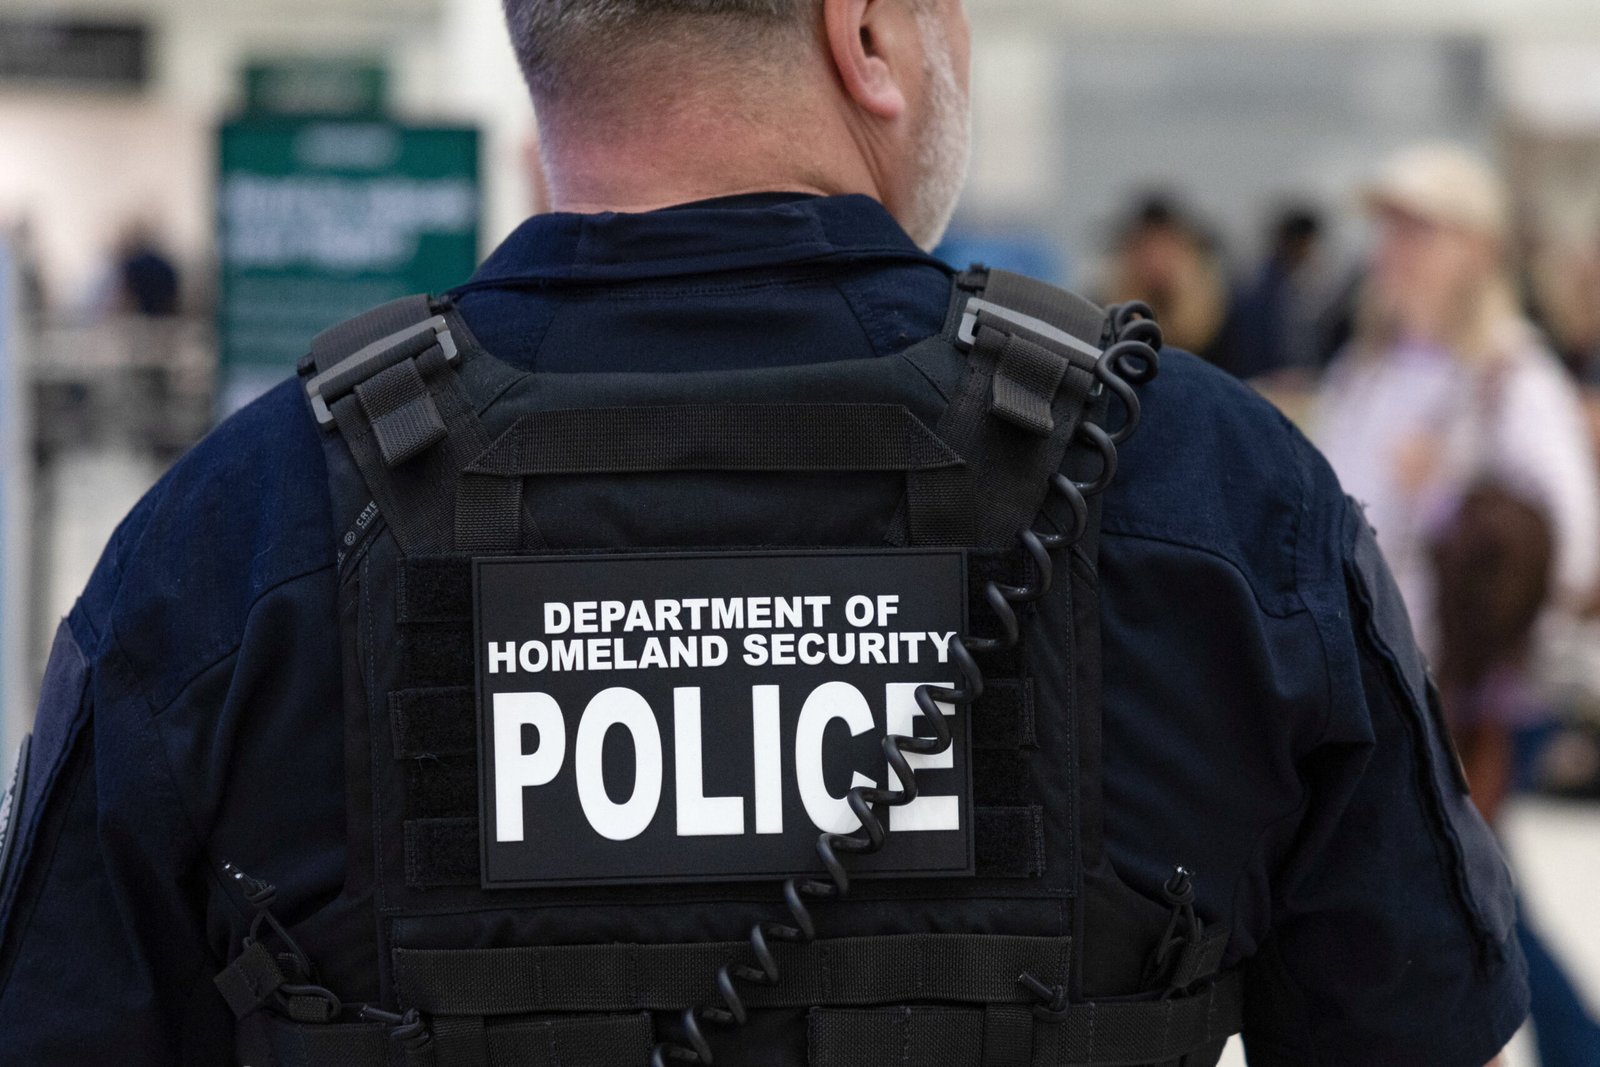
A data transparency group has published personal and operational files belonging to more than 40,000 Department of Homeland Security employees, marking the third major federal data leak in a month. Federal intelligence operatives, field agents, and cybersecurity personnel face compromised nonpublic organizational charts and sensitive assignment details following the unauthorized release.
Distributed Denial of Secrets released the records, drawing on material obtained by an entity calling itself the Department of Peace. The compromised trove covers workers across Immigration and Customs Enforcement, Customs and Border Protection, Homeland Security Investigations, and the Cybersecurity and Infrastructure Security Agency. Exposed files contain names, phone numbers, email addresses, and internal data indicating personnel assigned to undercover work, surveillance, computer forensics, and special operations.
The Department of Homeland Security stated in an official release that it was aware of a potential breach and was actively working to address the situation while ensuring employee protections. Hacktivist and search-tool developer maia arson crimew built a public interface for the database, which co-founder Emma Best stated was designed to boost congressional oversight and public records requests.
The Department of Peace harvested the information from the Okta sign-on service used by the agency, according to Distributed Denial of Secrets. Okta responded that its systems are secure and denied any compromise of its data or infrastructure. Reuters verified aspects of the leak by matching records for six employees with credit bureau files and dark web intelligence, alongside direct phone confirmations.
The incident follows a September breach involving Federal Bureau of Investigation personnel data and a Defense Department class-action lawsuit filed last week over exposed military records.