Fake Microsoft 365 Outage Notices Launch Credential Phishing Drive
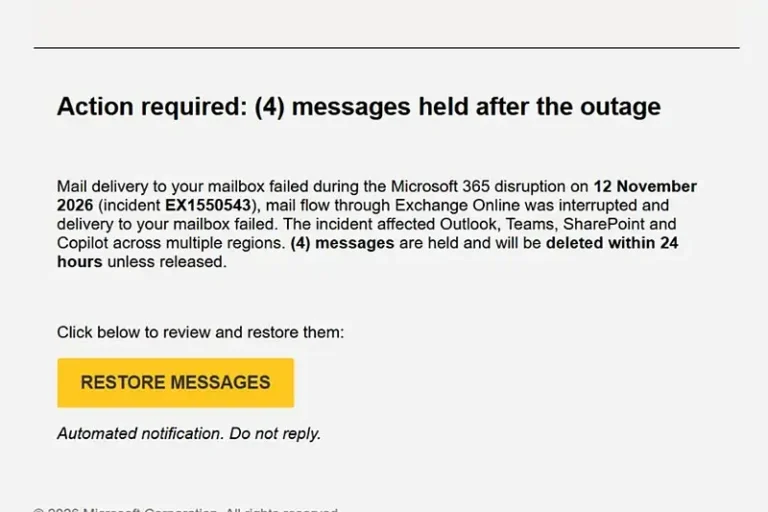
Microsoft Threat Intelligence detected an active phishing campaign on November 13 exploiting the recent Microsoft 365 service disruption. Corporate security teams and IT administrators across multiple United States sectors face fraudulent notifications impersonating official Microsoft communications and referencing legitimate Exchange Online incident EX1550543.
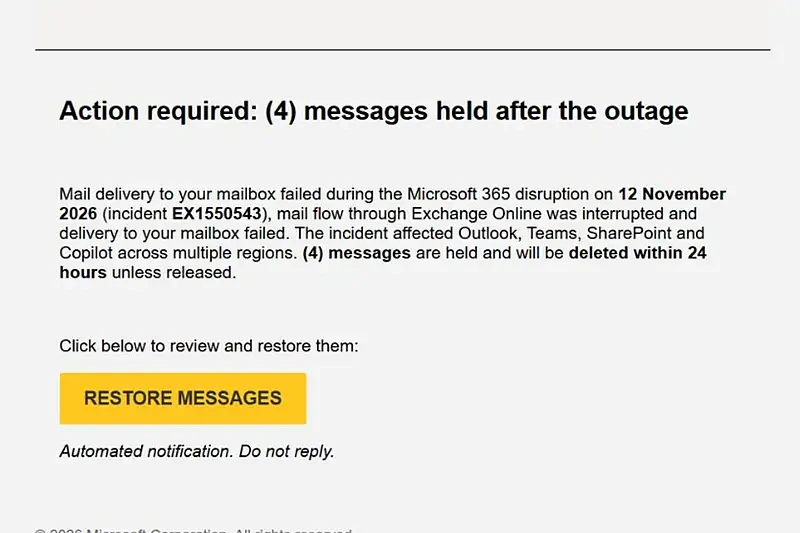
The fraudulent emails claim that messages were held during the November 12 outage and will be deleted within 24 hours unless recipients click to restore them. Observed subject lines follow a strict pattern using “Outage – [six-character code],” while sender display names deploy organisation-specific prefixes alongside “Outage Notification” or “Service Health.”
The operation relies on three specific sender domains, moments-notice[.]com, planetmaison[.]com, and newbooker[.]com, utilizing SendGrid click-tracking links to redirect targets to reallifeaccounting[.]com via the path /themelist0.html. Microsoft Threat Intelligence confirmed the activity matches patterns of credential phishing, though direct credential collection and malware delivery remain unverified.
IT departments can deploy Microsoft Defender for Office 365 Threat Explorer and Microsoft Defender XDR advanced hunting tools, including EmailEvents, EmailUrlInfo, and UrlClickEvents, to identify suspicious messages, analyze embedded URLs, and review user click activity.